BriefBox - Temporary Email Service
Overview
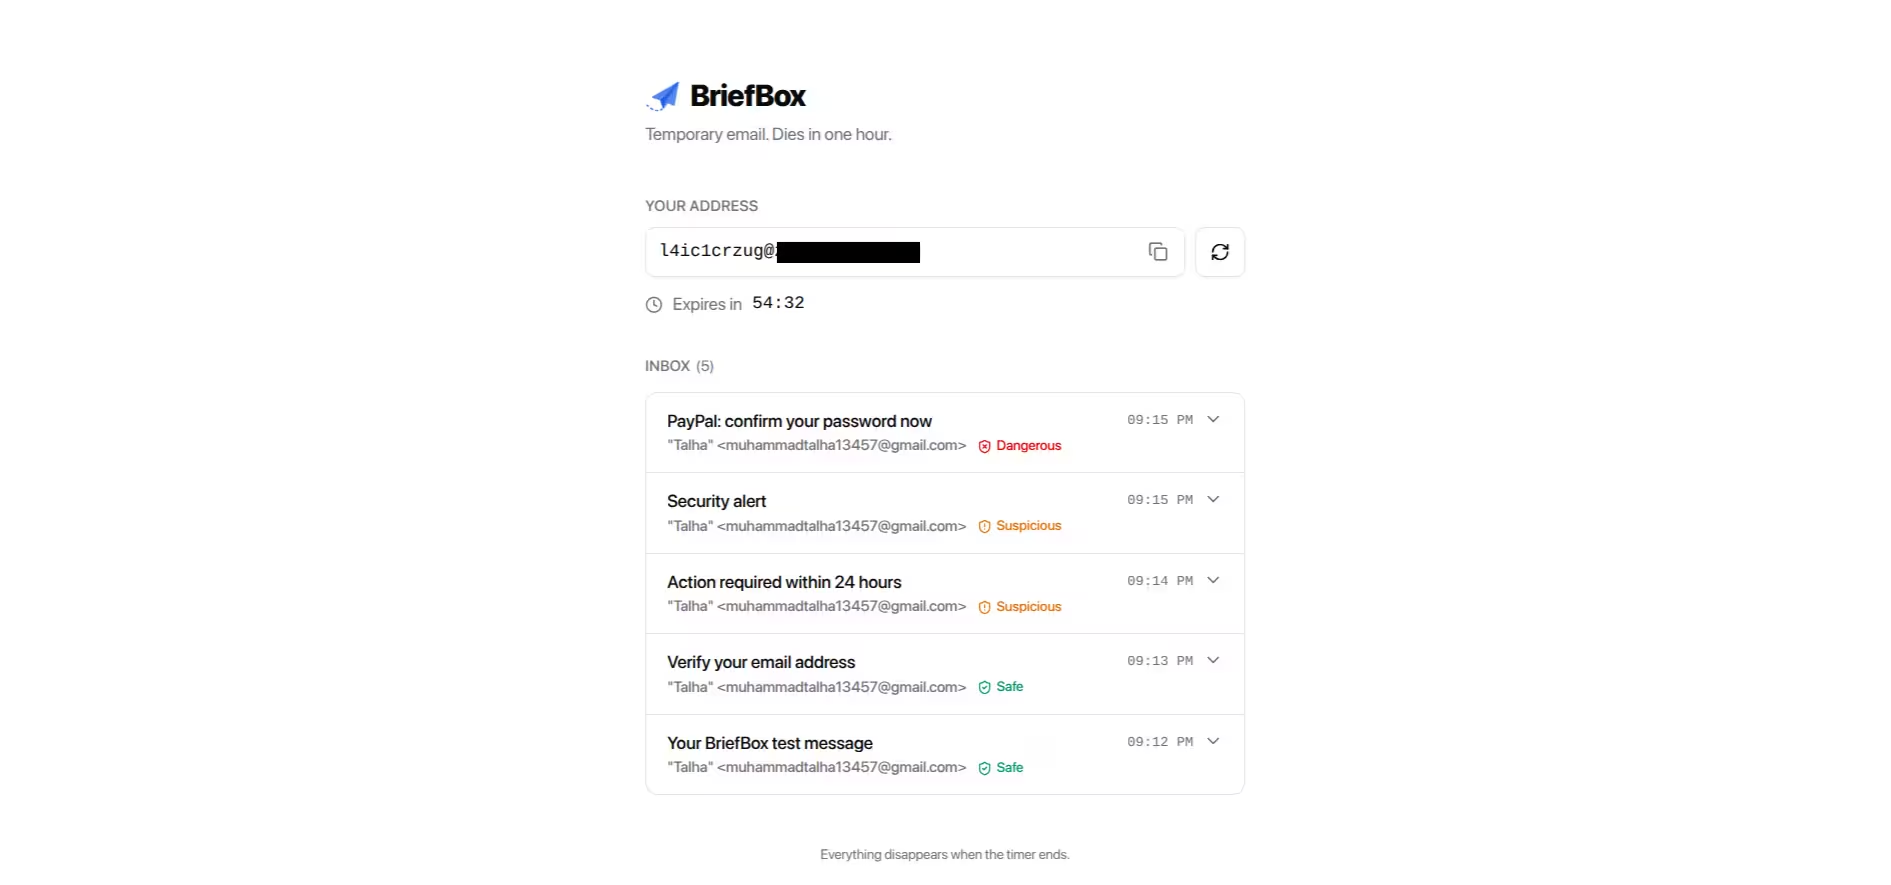
Anonymous disposable email service with one-hour self-destructing inboxes. Generates real addresses on a custom domain, receives inbound mail through Cloudflare Email Routing, scans messages for phishing signals, and stores everything in Redis only — no accounts, no permanent database.
Features
No signup / no login; Only cookie-based anonymous sessions only
One temporary email address per browser session
Exact 1-hour lifetime with live countdown timer
Automatic cleanup via Redis TTL for sessions and messages
Real inbound email on a custom domain via Cloudflare Email Routing catch-all
Cloudflare Email Worker forwards raw MIME to the Fastify webhook
MIME parsing with mailparser for subject, text, HTML, and links
Local rule-based safety scoring: Safe / Warning / Dangerous badges
Phishing heuristics for scam phrases, shady TLDs, IP links, shorteners, and brand mismatch
Sanitized HTML rendering in the inbox (DOMPurify)
Copy-to-clipboard for the temporary address
Inbox refresh via React Router revalidation
Rate limiting, helmet, CORS, and webhook shared-secret protection
PNPM + Turborepo monorepo with separate web and backend apps
Dockerfiles for web and backend production builds
Built with
Challenges & Solutions
Problem
Getting real mail into disposable addresses required more than a webhook endpoint
Solution
Configured Cloudflare nameservers, Email Routing, catch-all rules, and an Email Worker that POSTs raw messages to the backend with a shared webhook secret.
Problem
Early safety rules flagged normal product emails like “verify your email” as risky
Solution
Separated weak auth language from strong scam phrases, limited brand-mismatch penalties to credential-style links, and required shady link context before raising scores.
Problem
Needed ephemeral storage without building a full user/database model
Solution
Designed Redis-only keys for sessions, email-to-session reverse lookup, and per-message records, all with matching TTLs so data disappears with the inbox.
Problem
Session cookies created during loader requests were not reaching the browser
Solution
Captured Set-Cookie headers from API responses in the server-side client and forwarded them through the React Router loader response.